October, or Cybersecurity Month, is a good time to get your company's cybersecurity in order
In a nutshell
October is European Cybersecurity Month (ECSM), the annual EU and ENISA campaign to raise cybersecurity awareness.
73% of the targets of cyberattacks are essential or important entities as defined by NIS2.
The most common threats are still phishing and ransomware, but AI-enabled scams are increasing fast.
Only 45% of organizations communicate about cybersecurity to their staff on a regular basis, even though 74% of employees encounter suspicious messages.
It's worth finding out the state of your company's cybersecurity in concrete terms: a cybersecurity assessment or audit is often the best place to start.
A company’s cybersecurity refers to the practices, tools and expertise a company uses to protect its data, systems and operations from cyber threats. European Cybersecurity Month, held in October, is a good time to check how things stand in your own company. In this blog article, we briefly go through what ENISA's Threat Landscape 2026 report and the recent Eurobarometer survey tell us about the most common cybersecurity threats, why cybersecurity matters for every company, and how a cybersecurity audit can help you find out where you stand.
What is Cybersecurity Month?
Cybersecurity Month (European Cybersecurity Month = ECSM) is an annual EU campaign held every October. The campaign was launched in 2012 on the initiative of ENISA, the EU Agency for Cybersecurity, and is now supported by ENISA and the European Commission together with the member states and public and private sector actors. Its aim is to raise cybersecurity awareness among citizens and organizations and to provide ways to stay safe online. In Finland, Traficom's National Cyber Security Centre takes part in the campaign by sharing tips from the Nyt valppaana -network.
Why now is a good time to check your company's cybersecurity
According to a recent Eurobarometer survey:
74% of respondents have received suspicious emails, messages or calls in the past six months.
83% of respondents consider the consequences of a cyberattack to be serious for their organization.
Only 45% of respondents say their organization communicates about cybersecurity regularly, and only around half of the organizations have key cybersecurity measures in place.
In addition, according to ENISA's Threat Landscape 2026 report, public administration is the most targeted sector (32% of cases), and 73% of targets are essential or important entities as defined by NIS2.
In other words: there are plenty of cybersecurity threats, but many companies don't keep their employees regularly up to date on the company's cybersecurity matters and the latest threats. Security-aware employees help protect the company against many cybersecurity threats. The topic also matters from a regulatory perspective, for example, when your company is an essential or important entity under NIS2.
Other legislation is also making it increasingly important for companies to get to grips with cybersecurity. If the legal requirements are ignored, a company faces the risk of sanctions on top of the security risks. We have covered the Cyber Resilience Act (CRA) from the perspective of SaaS companies in an earlier blog article. The CRA is particularly timely, as its requirements have already entered into force or will do so soon; we covered this in another earlier blog article, CRA reporting obligations enter into force in September 2026.
Common threats: phishing, ransomware and ClickFix
Phishing is still the most common single threat. The attacker tries to trick the recipient into handing over credentials, payment details or other sensitive information through a message, link or website that looks genuine. You can protect yourself against phishing, for example, with strong passwords and multi-factor authentication (MFA), and by not clicking suspicious links. You can find more tips, for example, on the website of Victim Support Finland (RIKU).
Ransomware, in turn, encrypts an organisation's data and demands a ransom for releasing it. According to ENISA, ransomware was used in around 40% of financially motivated cyberattacks in 2025. You can also protect yourself against ransomware, for example, by not clicking suspicious links and by keeping your devices protected with antivirus software.
A technique called ClickFix, first observed in 2023, has also been on the rise. ClickFix tricks the user into running a malicious command themselves, for example through "I am not a robot" style buttons. The user is then asked to paste the copied text into the Run dialog on their own device (e.g. Windows + R). Traficom's website has guidance on recognizing and protecting against ClickFix scams, for both individuals and organizations (in Finnish).
AI is changing the threat landscape
ENISA points out in its Threat Landscape 2026 report that criminals are increasingly using AI, both to carry out scams and to spread disinformation. In just one year, AI-enabled foreign information manipulation and interference (FIMI) grew by 259%. This is worth taking into account in your own organization's preparedness: the traditional "check the sender's address" advice is no longer enough when AI can produce flawless language, convincing speech and even believable video content.
If you're interested in AI regulation in the EU more broadly, we have also written a blog article on the EU AI Act.
Making sure your company's cybersecurity is in order: the cybersecurity audit
Many companies assume their cybersecurity is at a sufficient level but have never actually checked. If risks haven't come up in your own operations yet, it's easy to settle into a false sense of security. But just because your company hasn't faced phishing attempts or other cyber risks in the past doesn't mean they won't appear in the future. Preparing for risks is the best way to prevent them from materializing.
A cybersecurity assessment or audit is a concrete answer to this: an external expert reviews your current practices, identifies the most obvious risk areas and provides a prioritized list of actions. This is often the most sensible first step before drawing up broader security guidelines or investing in new tools.
Security services and cybersecurity consulting: when to seek outside help
Not every company has its own cybersecurity team, and it isn't necessarily needed. When you do need cybersecurity expertise, bringing in external expertise can be a good solution. Situations where external security services or consulting may be needed include, for example:
your in-house expertise or resources aren't enough to build a comprehensive security program
NIS2 or other regulation requires measures whose scope is hard to assess on your own
your company has grown quickly and cybersecurity hasn't kept up
it has been a long time since the last cybersecurity assessment, or one has never been done
Cybersecurity services can be acquired in many forms: as a one-off audit, as ongoing consulting or as a cybersecurity expert hired to work as part of your own team. With us, you get a skilled cybersecurity expert who takes care of getting your company's security matters in order.
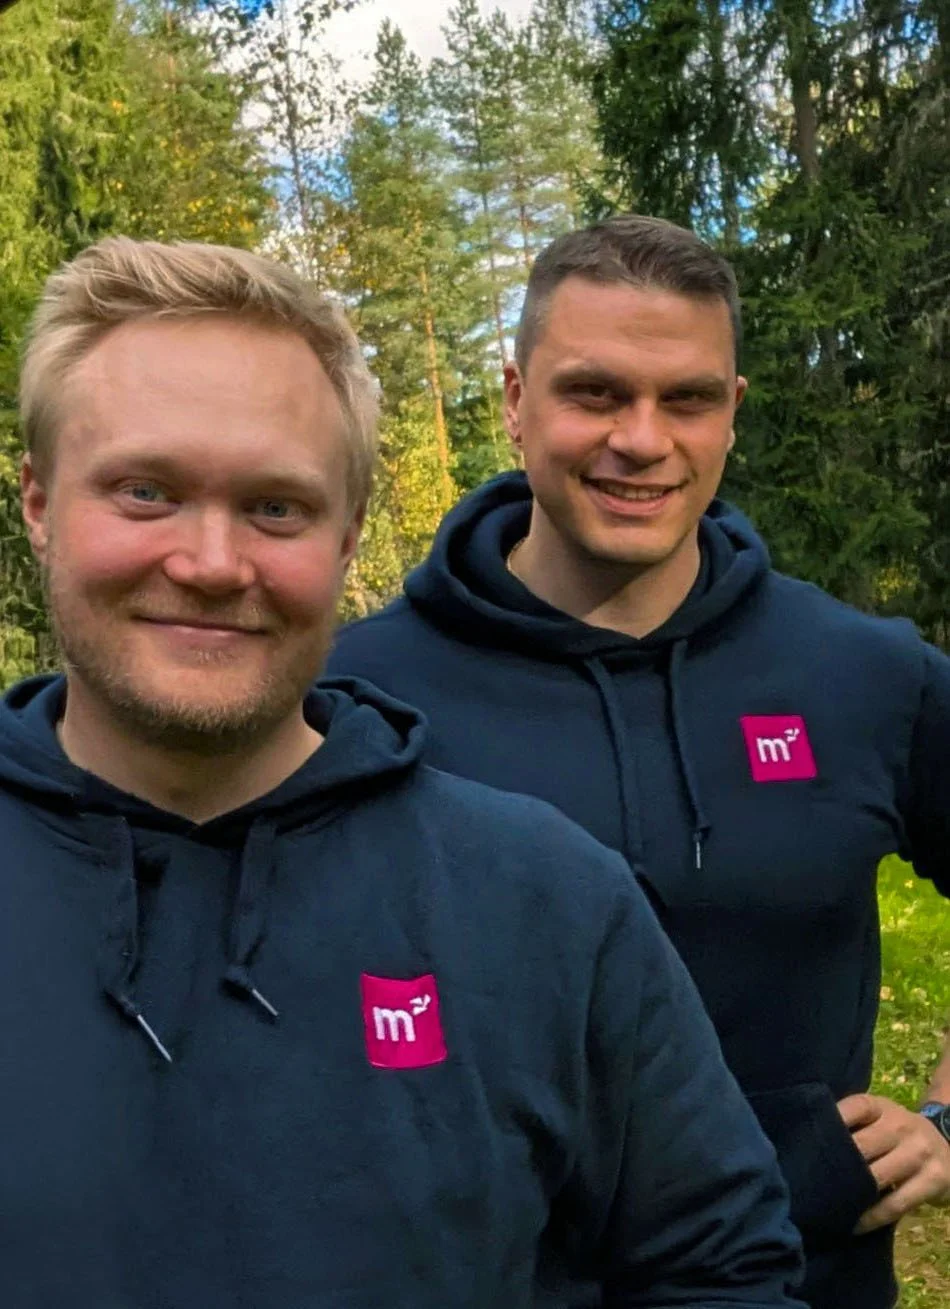
Sampsa (in the front) and Tero (in the back) can help find the best cybersecurity expert for your project!
Cybersecurity is not a one-off project
Cybersecurity Month is a good reminder to improve your security, but the topic shouldn't be forgotten when the month ends. Your company's cybersecurity requires continuous maintenance, attention to risks, the right expertise, and keeping that expertise up to date.
If you need cybersecurity consulting to map out your company's current situation, or a cybersecurity expert to strengthen your team, Marvel Consulting's consultants are happy to help. Get in touch and let's talk about your needs!